
UniFi Endpoint
Android OnlyFree·User Rating
 Analysis by ViaAPK
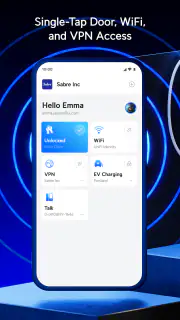
UniFi Endpoint is a business-focused Android app from Ubiquiti Inc. that aims to make connecting to a UniFi endpoint feel quick rather than technical. I approached it less like a general networking utility and more like a companion for people who already work with Ubiquiti equipment or have been given access to a UniFi environment. That distinction matters: its value depends heavily on the setup around it, so it is not the kind of app I would recommend to someone simply looking for a broad, all-purpose connection tool.
The app is free, rated for Everyone, and currently sits at a 4.6 average from around 5.7 thousand ratings. It has passed 100 thousand installs, which gives it a reasonable level of visibility among business users without making it feel like a mass-market consumer app. The store summary, “One-Click Connection,” describes the central appeal well, but it does not explain the practical questions I would have before installing it: when the shortcut is genuinely useful, what happens when access is not ready, and how much control I retain during a connection attempt.
What using UniFi Endpoint feels like in practice
My first impression is that the app is built around reducing steps. Instead of making me work through a long sequence every time I need to reach a managed endpoint, it places the connection task at the center. That simplicity is welcome in a workplace where the same person may need to connect repeatedly during the day, especially when the alternative is remembering several details or navigating through a larger management workflow.
There is an important difference between simple and universal here. UniFi Endpoint makes the most sense when an organization has already chosen the UniFi ecosystem and has a clear way for a user to reach the relevant endpoint. It does not replace the planning, configuration, or access decisions made by whoever manages that environment. I would treat it as the user-facing part of an existing setup, not as a standalone solution for discovering and organizing every network or business device nearby.
That makes the app particularly suitable for staff who are not network specialists. A technician can prepare the environment, while an employee uses the app for the final connection without needing to understand every underlying setting. In my view, this is where the one-click idea has real value: it can turn a technical process into a repeatable routine, provided the account and endpoint arrangements have already been handled properly.
A realistic workday example
Imagine a small office where a team member moves between a desk, a meeting room, and a temporary work area. Each location may require access through a UniFi-managed endpoint. With the app ready and the correct access already arranged, the employee can open it when needed and start the connection without asking the administrator to walk through the process again.
The benefit is not only speed. It is consistency. A repeatable connection path can reduce the temptation to use improvised alternatives, such as joining an unfamiliar network or relying on a personal workaround. That said, I would not confuse a shorter connection flow with automatic proof that the destination is appropriate. The user still needs to recognize the organization’s approved environment and stop if the request or endpoint looks unexpected.
News Worth Your Time
Brain Test 2 Suits the Stop-and-Start Rhythm of Modern Phones
Google Play Games Makes Android Gaming Easier to Navigate, Not Easier to Love
WhatsApp Under Pressure: How Well It Recovers When Messages Fail
UNO!™ Beyond the Table: How Rivalry Keeps Players Coming Back
LinkedIn: Dominating the Professional Networking Arena
Unlocking the Full Potential of Pixel Art - Color by Number
Roblox: A Creative Revolution in Gaming
Why Gallery Stands Out in the Photo App World
How Pi Network is Revolutionizing Social Cryptocurrency
Google TV's Ecosystem Strategy: Redefining Streaming
How Little Panda: Princess Makeup Thrives with New OS Updates
Why Decor Life - Home Design Game Stands Out in Creative Simulation
This is also where trust becomes part of the review. A connection app sits close to sensitive activity, so I would not judge it only by how quickly it opens a session. I would also ask whether the user understands what is happening, whether access can be withdrawn, and whether the organization has explained the purpose of the connection. The app can make a legitimate workflow easier, but clarity around that workflow still belongs to both the software and the administrator.
Who benefits most from the focused design
I see the strongest fit for employees, contractors, students, or support staff who have been invited into a UniFi-based environment and need a convenient endpoint connection rather than a full network administration console. It can also suit a small business that wants a simple handoff between technical setup and everyday use. The free price removes one obvious barrier for organizations testing whether this kind of endpoint workflow fits their routine.
I would be more cautious about recommending it to someone who has no UniFi equipment, no administrator, or no clear endpoint invitation. In that situation, the app may feel confusing because the important part of the experience is not just the installation. The surrounding account arrangement and endpoint availability determine whether the central action is useful. If your main goal is monitoring home devices, changing router settings, or comparing nearby wireless networks, a conventional router-management or diagnostic app is likely a better match.
Trust starts with the access relationship
Because the app is connected to business access, I would install it only when I understood who had authorized the connection and why. That is not a criticism of UniFi Endpoint; it is a sensible habit for any tool that can place a device inside an organization’s working environment. A one-tap action is convenient, but convenience should not remove the user’s responsibility to verify the source of the invitation and the endpoint being used.
In practical terms, I would confirm the organization’s instructions through a known channel rather than accepting an unexpected request from an unfamiliar contact. I would also avoid setting up the app on a shared phone unless the owner of that device understands the account arrangement. These small checks are more valuable than treating the app’s short connection flow as a security guarantee.
The developer is Ubiquiti Inc., a name closely associated with UniFi networking products. That context helps explain why the app is so specialized, but it should not lead users to assume that every Ubiquiti product behaves identically. I would still read the organization’s own instructions, check the account currently in use, and keep the app updated. The current release is version 4.0.3, and the app requires Android 7.0 or later, so compatibility is worth checking before planning a rollout across older devices.
Controls I would check before relying on it
When I review an access-oriented app, I look for visible choices rather than making assumptions about what happens behind the scenes. Before using UniFi Endpoint for work, I would check which account is active, what endpoint the app is asking me to reach, and whether the organization provides a clear way to end or revoke access. Those are the controls that affect daily confidence more than the simplicity of the opening screen.
I would also pay attention to Android’s permission prompts and system indicators during setup and use. A permission request should have an understandable connection to the task being performed. If a prompt appears unexpectedly, I would pause and ask the administrator what it is for instead of approving it automatically. This is a useful habit because the app’s business context may involve access decisions that are more important than the wording of the store summary suggests.
Another practical check is account separation. If I used the app for more than one organization, I would want to know exactly which account or environment I was entering before tapping the connection control. Mixing workspaces is an easy way to create confusion, especially on a personal phone. I would keep the organization’s naming conventions clear and review the active identity whenever the app had been unused for a while.
The most important control is knowing which organization you are connecting to before using the shortcut. That sounds basic, but the whole point of a one-action workflow is to remove friction. Removing friction is helpful only when the destination is already familiar and authorized.
Data-sensitive moments deserve extra attention
There are several moments when I would slow down. The first is installation and initial setup, when the app may ask for access or account information. The second is switching between endpoints or organizational environments. The third is using it on a device that other people can unlock. In each case, I would look at the screen carefully, read prompts in full, and avoid treating a fast path as a reason to skip verification.
I would also separate the app from the organization’s broader data practices. An endpoint connection may expose business resources, but the app itself is only one part of that arrangement. The employer, school, or service provider may have its own rules for account activity, device management, and retention. I would ask the administrator which activity is logged, who can remove access, and what happens when a person leaves the organization. Those answers are essential to informed use, and they should come from the responsible organization rather than guesswork.
On a personal device, the trade-off is more noticeable. The convenience of connecting to work resources may be worth it, but I would want a clear boundary between personal use and business access. I would avoid lending the phone while an organizational session was active and would use the device’s normal lock and account protections. If the organization requires controls that feel too invasive for a personal phone, I would ask whether a company-managed device is the better option.
One non-obvious advantage of a focused app is that it can make the approved route more visible. When employees have a clear, recognizable way to connect, they may be less likely to search for unofficial alternatives. The trade-off is that a focused app can also hide complexity from the user. If something fails, the person may not know whether the problem is the phone, the account, the endpoint, or the organization’s configuration. Good onboarding and a reachable administrator remain important.
Where the one-click approach can stumble
The biggest weakness is dependency. If the endpoint is unavailable, the account is wrong, or the organization has not completed its configuration, the app cannot turn an incomplete setup into a working connection. A user who expects the app to discover and solve everything may be disappointed. I would make sure the administrator has tested the intended workflow before asking a large group of employees to depend on it.
There is also a support trade-off. A conventional management app may expose more diagnostic information, while a streamlined endpoint app may keep the interface cleaner at the cost of explaining failures less clearly. For a network professional, that can make troubleshooting feel limited. For an ordinary employee, the same restraint may be a benefit because it avoids presenting settings they should not change.
Another limitation is scope. I would not choose UniFi Endpoint as a substitute for a full UniFi administration tool when I need to configure equipment, inspect detailed network behavior, or manage a larger infrastructure. Nor would I select it over a general remote-access product when the organization uses a different technology stack. The best alternative depends on the existing environment: a UniFi administrator needs management depth, while an invited user may prefer this narrower connection experience.
Battery, connectivity, and device state can also affect any mobile connection workflow. I would keep the phone updated, avoid testing for the first time during an urgent meeting, and make sure I had a backup contact for access problems. That is a practical tip that is easy to overlook: the app can simplify normal use, but it should not be the only plan for a time-sensitive business connection.
How I would introduce it to a team
I would start with a small pilot rather than installing it everywhere at once. The pilot group should include one ordinary user and one person responsible for access, because they will notice different problems. The user can judge whether the connection flow is understandable, while the administrator can confirm that the right endpoint and account are being used.
Before wider adoption, I would write a short internal instruction using plain language: where to get the app, how to identify the correct organization, what a normal connection request looks like, and whom to contact when it fails. I would include a reminder not to approve unexpected prompts or share account access. This kind of guidance adds more trust than simply telling people that the app is fast.
I would also define an offboarding step. When an employee changes role or leaves, someone should know how to remove their access and what the user should do with the app. The exact procedure depends on the organization’s setup, so I would not invent a universal sequence. The important point is that access should be treated as temporary when the work relationship is temporary, rather than left untouched because the app is no longer being opened every day.
My verdict for careful users
UniFi Endpoint is a sensible choice when you already belong to a UniFi-managed environment and want a direct, repeatable way to reach an approved endpoint. I like its focused purpose and the way it can reduce unnecessary steps for people who should not be changing technical settings. Its free availability and Everyone rating also make it easy to consider for a broad workplace audience, while the Android 7.0 requirement keeps it usable on many older devices.
My recommendation comes with a clear condition: understand the account, endpoint, and organization behind the connection before relying on the shortcut. The app should make an authorized workflow easier, not replace authorization or explain away unexpected behavior. I would choose it for a prepared UniFi deployment, especially where ordinary staff need a simple entry point. I would skip it for general network discovery, deep administration, or environments built around another platform.
After using it, I see the product’s strength as disciplined simplicity rather than a large feature set. That is a good trade when the surrounding setup is sound. It is a poor trade when users need detailed diagnostics or have no one to answer access questions. For the right audience, UniFi Endpoint can turn a technical connection into a manageable daily action; for everyone else, a broader networking or remote-access option will likely be more honest about what they need.
Pros
- Centralized visibility for UniFi-connected endpoints
- Useful device health and connectivity insights
- Helps identify network issues more quickly
- Clean interface suited to UniFi administrators
- Supports proactive monitoring of managed devices
Cons
- Requires a UniFi network and compatible management setup
- Limited value for users outside the UniFi ecosystem
- Some features depend on controller configuration
- May generate alerts that need manual investigation
- Advanced monitoring can require paid UniFi services
FAQ's for UniFi Endpoint
What is UniFi Endpoint and what is it used for?
UniFi Endpoint is designed to help organizations manage and monitor compatible UniFi-connected devices and endpoints from a centralized environment. Depending on the UniFi products installed, administrators may use it to review device status, identify connectivity issues, apply configuration changes, and keep track of network or security equipment. Its usefulness depends heavily on the UniFi ecosystem and account permissions available to the user.
Can I use UniFi Endpoint without owning UniFi equipment?
The application is primarily intended for users who already operate compatible UniFi hardware or services, such as UniFi networking, access, camera, or other supported endpoint products. Without a UniFi setup, there may be little or no practical functionality available after installation. Before downloading, check whether your specific device and UniFi console are supported, because features can vary according to the hardware model, software version, and administrator configuration.
Do I need a UniFi account or administrator access to use the app?
In most cases, you will need a valid UniFi account or access granted by an organization administrator to connect to the relevant console or endpoint environment. What you can see and change depends on your assigned role. Owners and administrators generally receive broader management controls, while invited users may only be able to view status or perform limited tasks. Account permissions should be confirmed before installation.
Does UniFi Endpoint work remotely, or must I be connected to the local network?
Remote access may be available when your UniFi console is properly configured for cloud access and your account has permission to reach it. Local access can also be possible when your phone is connected to the same network as the supported UniFi equipment. However, availability depends on the console model, firmware, internet connection, and security settings. Some management actions may require a stable connection and could be unavailable during outages.
What permissions and phone requirements should I expect?
UniFi Endpoint may request permissions needed for account authentication, network discovery, notifications, or device-related management features. The exact requests can differ between Android and iOS and may change with future updates. A modern, supported version of the operating system is recommended, along with reliable Wi-Fi or mobile data. Users should also keep the UniFi application and connected hardware updated to reduce compatibility and security problems.